SMB NTLM Authentication Rate Limiter
Windows Server Preview Build 25075 的新功能
配置:
Set-SmbServerConfiguration -InvalidAuthenticationDelayTimeInMs *n*
Ubuntu nftables 配置zerotier SNAT
zerotier的网段为10.234.0.0/24
sudo nft add rule nat POSTROUTING ip saddr 10.234.0.0/24 oif eth0 masquerade
sudo nft add rule filter FORWARD ip saddr 10.234.0.0/24 oif eth0 accept
Firefox 扩展 Resource Override
规则:
- recaptcha重定向到国内服务 :
{
    "v":1,
    "data":[
        {
            "id":"d1",
            "matchUrl":"*",
            "rules":[
                {
                    "type":"normalOverride",
                    "match":"https://www.google.com/recaptcha/*",
                    "replace":"https://recaptcha.net/recaptcha/*",
                    "on":true
                }
            ],
            "on":true
        }
    ]
}
Linux 上添加自定义 CA 证书
当使用内部 CA 签发的证书时,需要将 CA 根证书添加到系统信任存储中,否则 curl、wget、openssl 等工具会报证书错误。
假设证书文件为 my-ca.crt(PEM 格式),以下按发行版说明操作方法。
深信服HCI 迁移虚拟机失败:拷贝磁盘数据异常
从SCP(HCI)迁移虚拟机到Vsphere,报错"迁移虚拟机失败:拷贝磁盘数据异常"
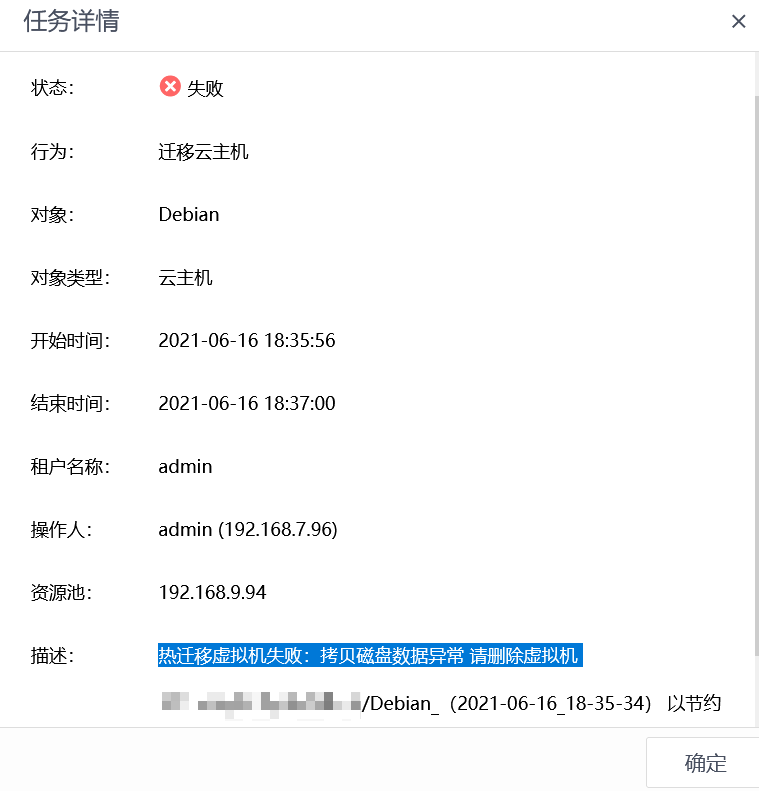
迁移失败
原因是目前我在用的vSphere版本为7.0.2,深信服HCI没有配置对应的vddk版本信息,补充即可
在不重启或者注销的情况下,更新AD组成员身份
- 计算机组成员身份更新
rem 用管理员身份运行
klist.exe -li 0x3e7 purge
gpupdate /force
- 用户组成员身份更新
rem 当前用户身份运行
klist purge
通过powershell查看谁重启了服务器
通过powershell可以很方便的查询谁重启过服务器,对于Server Core尤其方便。服务器重启的事件ID为1074.查询命令为
Get-WinEvent -LogName system | Where-Object ID -eq 1074
安装OpenSSH for Windows
下面是在powershell中操作的命令记录
choco install powershell-core -y
choco install openssh
cd C:\Program Files\OpenSSH-Win64
Set-ExecutionPolicy RemoteSigned
#设置默认shell为powershell
.\Set-SSHDefaultShell.ps1 -PathSpecsToProbeForShellEXEString "\$env\:userprofile\downloads\*.exe;c:\Program Files\PowerShell\*\P\*.exe;c:\windows\system32\*"

#配置认证用authorized_keys
#系统管理员需要把authorized_keys保存到C:\ProgramData\ssh\下面,并命名为administrators_authorized_keys
#配置authorized_keys权限
icacls.exe ""$env:ProgramData\ssh\administrators_authorized_keys"" /inheritance:r /grant ""*S-1-5-32-544:F"" /grant ""SYSTEM:F""
# 大工完成
在alpine Linux上运行 besttrace
在 alpine Linux上运行 besttrace时,报错no such file or directory,应该是缺少库文件,安装gcompat解决。
微软拼添加小鹤双拼方案
微软自带输入法支持添加自定义双拼方案了。网上搜索了一下,通过注册表添加最方便。导入注册表文件即可